MakeSense
HTB Medium Linux machine: a password leaked in a voice message, a forged client-side-encrypted payload that turns into stored XSS and a new WordPress admin, and root through an OCR service that saves recognized text as a PHP file
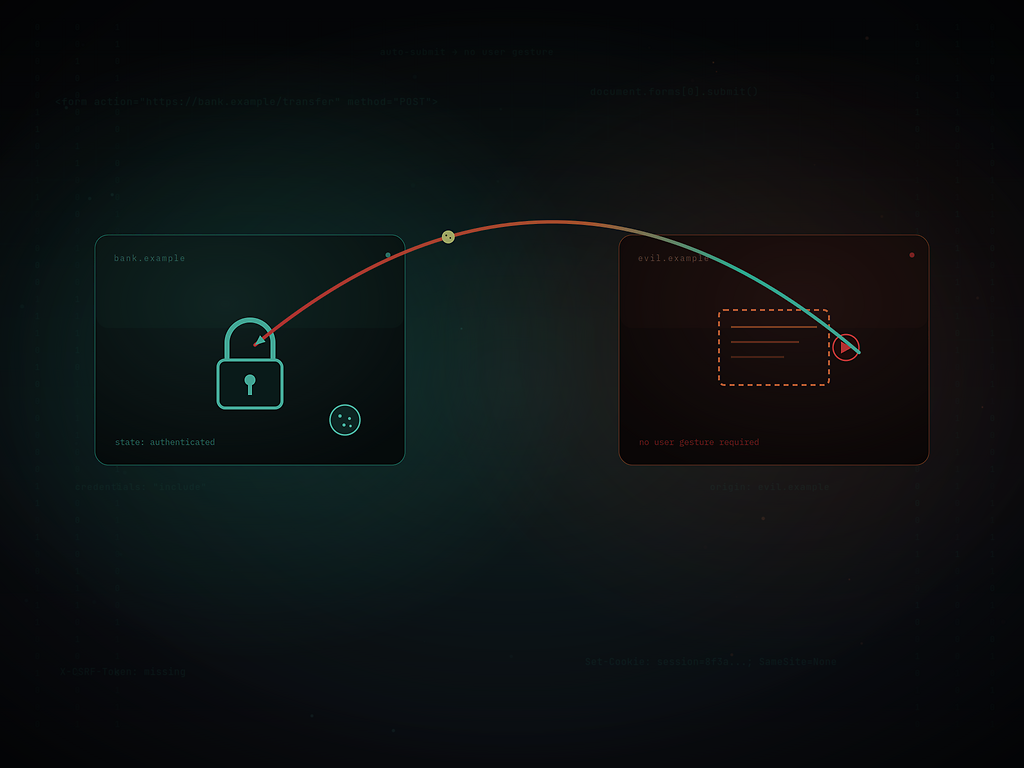
CSRF (Cross-Site Request Forgery)
What I learned after completing CSRF path in Portswigger